Frontier AI Models and Cybersecurity
The new frontier AI models: more capable than ever, and an unprecedented challenge for cybersecurity
In just one month, OpenAI, Anthropic and Google have released their most advanced models. The three share more than raw power: their own creators have chosen to limit access to their cybersecurity capabilities. What they offer, what risks they pose, and why professionals who understand both worlds will be increasingly in demand.
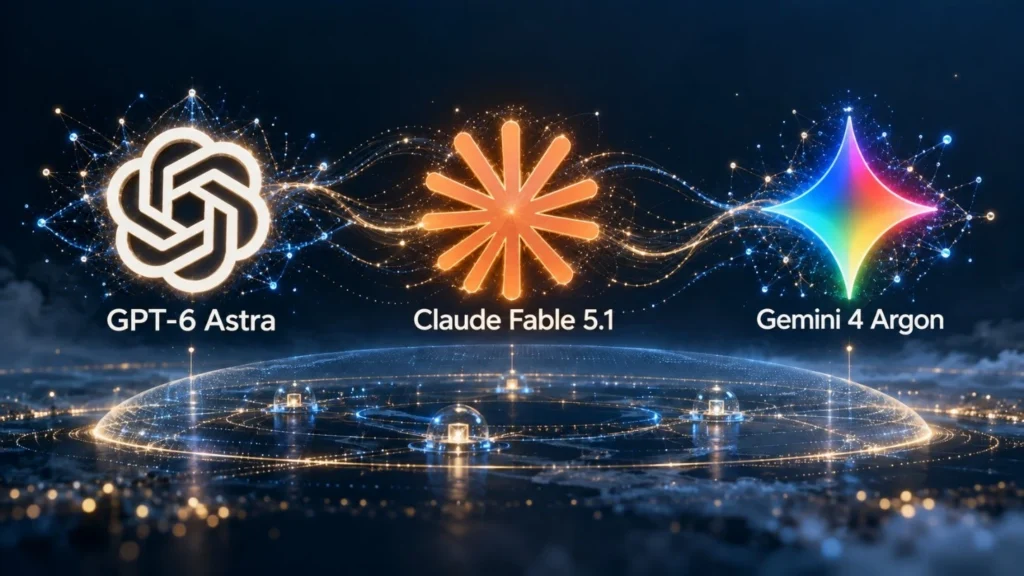
September 2026 will go down as one of the most intense months in the recent history of artificial intelligence. In a matter of weeks, three of the leading AI labs unveiled new frontier models, systems that rank among the most capable available today. And the message that came with these launches was not just “look what they can do,” but also a warning: the greater their capabilities, the more attention must be paid to who can use them, for what purpose, and under what controls.
That shift in tone says a lot about the moment we are living in. AI no longer just answers questions: it carries out tasks, writes and reviews software and, in expert hands, can help find vulnerabilities in computer systems. That same capability can be used to protect or to attack.
Three models, one shared concern
GPT-6 Astra, from OpenAI
OpenAI introduced GPT-6 Astra as a limited preview on September 3 and opened it to the general public the following day. Its big bet is autonomous task execution: according to CNBC, it excels at computer use, software engineering, professional work and science. Axios notes that it is designed to work directly inside software, rather than simply recommending what a person should do.
The most relevant detail for cybersecurity is a different one: OpenAI acknowledged that Astra is its first model to reach its internal “Critical” cybersecurity threshold. The company delayed the launch to add safety testing and opted for staged access: its most powerful capabilities in this area were reserved for a small group of trusted testers.
The shift is significant. Security is no longer just a layer added after a model is developed; it becomes part of the strategy that determines how the model is deployed.
Claude Fable 5.1 and Claude Mythos 5.1, from Anthropic
On September 1, Anthropic launched Claude Fable 5.1 and Claude Mythos 5.1, which share the same underlying model but come with different levels of safeguards and access.
Fable 5.1 is available to the general public, while Mythos 5.1 is offered only through trusted access programs designed for cybersecurity and the life sciences.
Here is how it works: Fable 5.1 applies automatic checks to every request, and many of the requests it blocks are answered by a less capable model from the company. According to MacRumors, Fable 5.1 can be used to discover software vulnerabilities, but not to develop exploits that take advantage of them.
Version 5.1 also fixed a practical problem with its predecessor: Anthropic says its new cybersecurity safeguards produce 60% fewer false positives, meaning they block legitimate work less often.
This model was also at the center of an episode that illustrates the geopolitical dimension of advanced AI. In June 2026, Anthropic temporarily suspended access to Fable 5 and Mythos 5 to comply with US Department of Commerce export controls. The restrictions were lifted on June 30 and access was restored on July 1, according to the company’s statement.
Gemini 4 Argon, from Google
The most recent of the three, announced on September 30, is built for long, multi-step tasks in software engineering, defensive cybersecurity and enterprise work. Google trained it specifically for cyber defense: according to BetaNews, the model can autonomously find, validate and fix critical software vulnerabilities.
Its access strategy is the most striking. Argon is being rolled out first to a select group of cybersecurity defenders through the Fairwind Program, and for them and for Google’s internal teams it is offered without the usual cybersecurity guardrails, so they can make full use of its defensive capabilities.
Google has not given a date for wider availability, and for now it is not available to free users.
The advantages: a new generation of tools
Beyond the performance figures, these models reflect a deeper shift: AI is moving from conversation to action.
In software development, the change is already tangible. Google says Argon is already working inside the company on large-scale code migrations, including the move from C/C++ to Rust, a language that reduces certain types of security bugs.
For security teams, the promise is enormous. A model capable of reviewing millions of lines of code, detecting flaws and proposing fixes can help close vulnerabilities before anyone exploits them. Google even claimed that Argon found a bug in hospital software, a clear example of its defensive potential.
In practice, these models can support security teams on three fronts:
- Code review: detecting flaws such as buffer overflows, SQL injections or misconfigurations before software reaches production.
- Incident response: analyzing large volumes of logs and network telemetry to correlate anomalies and speed up the containment of an attack.
- Controlled penetration testing: simulating authorized attacks to assess an application’s resilience before deployment.
It is precisely this last capability that reveals one of the main challenges of this new generation of artificial intelligence: dual use.
The cybersecurity problems
Giving an AI system permission to read information and take actions introduces risks that conventional firewalls are not designed to stop.
These are the main ones.
1. The dual-use dilemma
This is the core problem. The ability to find a vulnerability in order to fix it is the same ability that makes it possible to find it in order to exploit it. Anthropic puts it bluntly: without robust safeguards, these models’ advanced capabilities in cybersecurity and biology could be used to launch large-scale cyberattacks. That is why all three labs have opted for staged access models.
2. Who decides who is “trusted”?
Restricted access programs raise difficult questions. What criteria make an organization a “trusted defender”? What happens to security teams in countries, companies or institutions that are not part of these programs? In Anthropic’s case, according to MacRumors, access to Mythos 5.1 is limited to US companies and individuals taking part in its trusted programs. The concentration of the most advanced defensive capabilities in a few hands is, in itself, a subject of debate.
3. Agents that act, new attack surfaces
When a model can browse the internet, open files and carry out actions on a computer, a specific risk emerges: indirect prompt injection. An attacker can hide instructions in a web page, an email or a document so that the agent executes them without its user knowing. It is no coincidence that Google presents Argon as its most resistant model yet against this type of attack: it is one of the industry’s biggest concerns.
4. Monitoring what cannot be seen
An autonomous system is only safe if what it does can be monitored. This is where new challenges arise. GPT-6 Astra uses a reasoning technique called recurrent depth that improves efficiency but partially or fully hides the model’s chain of reasoning. OpenAI itself acknowledged that Astra was harder to monitor in tests designed to check whether it could evade oversight. Google, for its part, is deploying systems that monitor Argon’s reasoning and actions and halt its execution when necessary.
5. Imperfect safeguards, in both directions
Safeguards can fail in two ways: by letting dangerous uses through or by blocking legitimate ones. The second is also a security problem, because it slows defenders down. Fable 5.1’s 60% reduction in false positives shows that the labs are trying to fine-tune that balance, but also that earlier versions blocked a great deal of legitimate work.
What organizations should do
For any company or institution looking to take advantage of these models, a few basic practices are essential:
- Least privilege: give AI agents only the permissions they strictly need.
- Human approval for critical actions, such as transfers, system changes or sending sensitive information.
- Treat all external content as untrusted, especially when an agent reads web pages, emails or third-party documents.
- Logging and auditing of what agents do.
- Data classification, to decide which information can pass through these tools and which cannot.
- Team training, because technology is moving faster than internal protocols.
Adopting AI agents should not be seen solely as a productivity decision.
It is also a security decision.
A growing talent gap
If these launches make one thing clear, it is that the line between artificial intelligence and cybersecurity is blurring. Organizations need professionals who understand how these models work, how to integrate them securely and how to defend against those who use them with malicious intent.
This hybrid profile opens up two complementary paths. Those who want to explore in depth how these systems work, how they are evaluated and how they are governed will find in the Doctorate in Artificial Intelligence. UNADE a space to generate original knowledge about one of the technologies most transforming the world. And those who want to specialize in protecting systems, data and organizations in this new landscape can do so with the Master’s in Cybersecurity UNADE.
The frontier is also a responsibility
As a journalist and communication specialist, I find it significant that the creators of these models are the first to warn about their risks. It means the conversation has matured: it is no longer only about what artificial intelligence can do, but about who can use it, for what purpose and with what controls.
That conversation cannot be left to the labs alone. It needs researchers, security professionals, legal experts, policymakers and informed citizens.
The more capable these tools become, the more valuable the human judgment that decides how to use them.
Author
Dr. Ruth Gómez
Journalist and political scientist, expert in human behavior and specialized in communication.
Strategic advisor for doctoral education campaigns.
Universidad Americana de Europa (UNADE)
LinkedIn
This article is part of UNADE AL DÍA, the academic outreach initiative of Universidad Americana de Europa that analyzes the trends transforming higher education, employability and professional leadership in a global context.